
Govern the Software Factory
Your software factory was built for people. Extend it to agents.
Jenkins, GitHub Actions and your scanners each govern themselves. CloudBees Unify sits above them, so you can see what shipped, who approved it and what’s at risk, without migrating a pipeline.
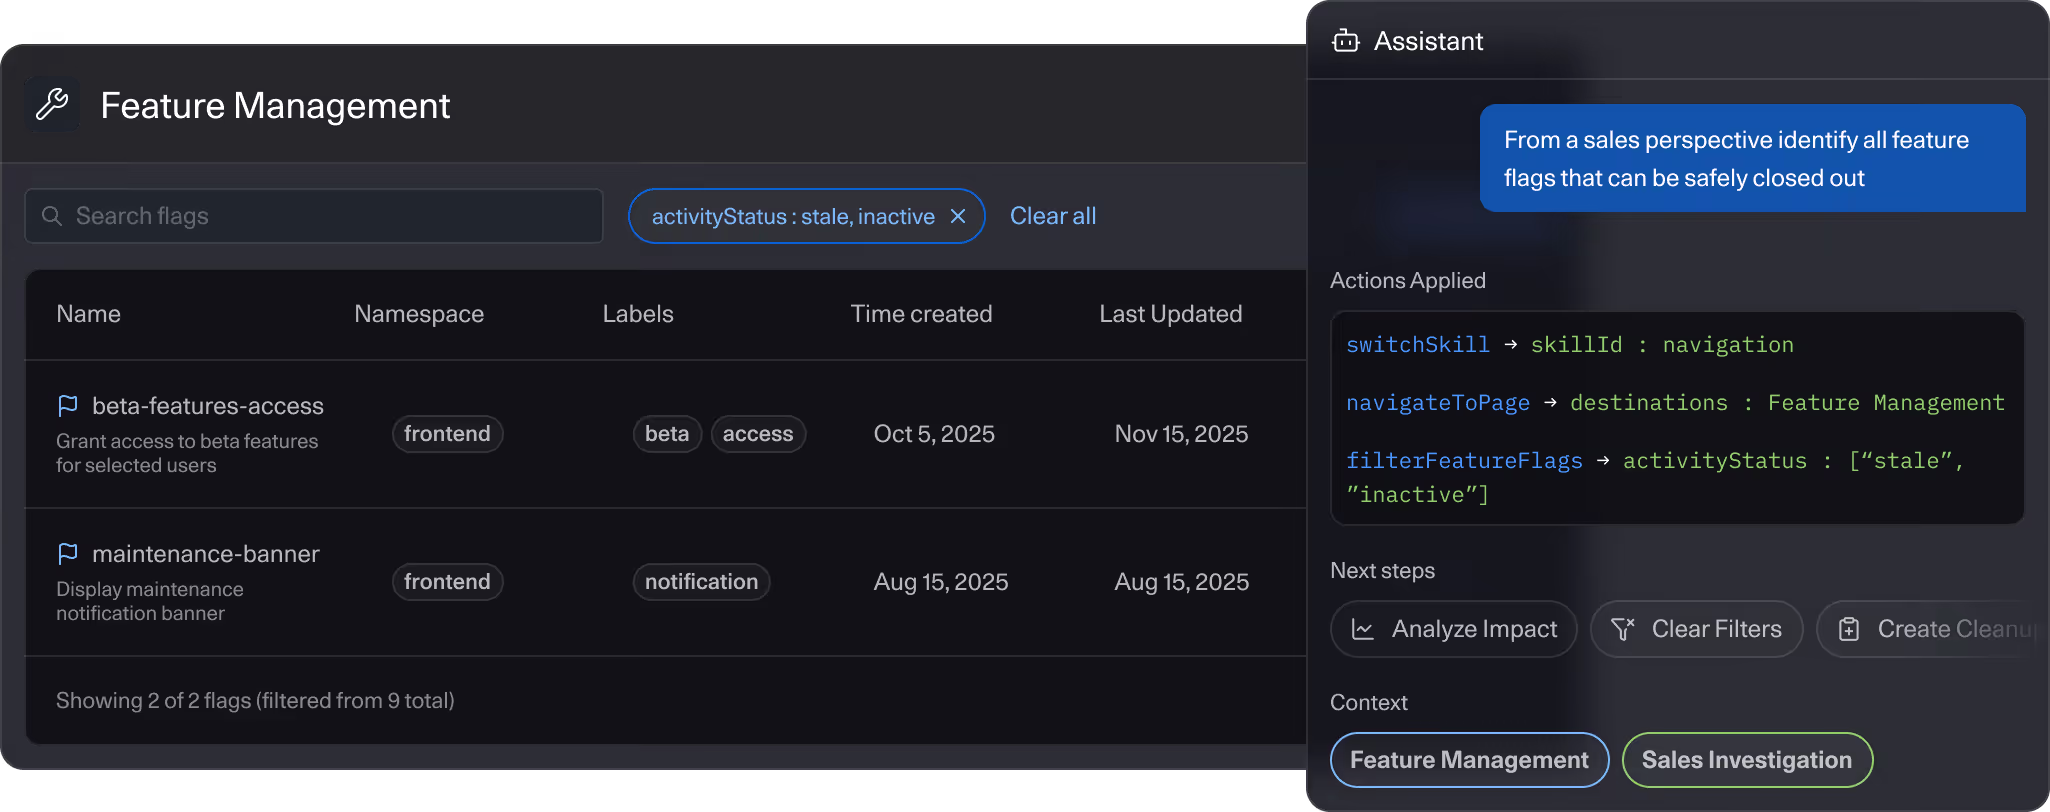
The gates didn’t break. The assumption behind them did.
Your checks, gates and approvals were designed for people working at human speed. Each tool still reports green on its own. But ask which controls ran on last week’s release, which services it touched or who signed off, and someone spends days piecing the answer together from four systems. Coding agents now send far more change through that same process.
Where the system breaks:
- Old access, new speed. Agents run on service accounts scoped wide years ago. Same reach, now moving at machine speed.
- Checks stopped keeping up. Tests and gates were sized for human-speed change. At agent speed, green means they ran, not that they fit.
- Review became a rubber stamp. One engineer clears 50 agent PRs in an afternoon. The check passes. The protection doesn’t.
- Nobody’s name on it. A service account six teams share isn’t an owner. The log shows what happened, not who decided.
Close the seams. Keep your tools.
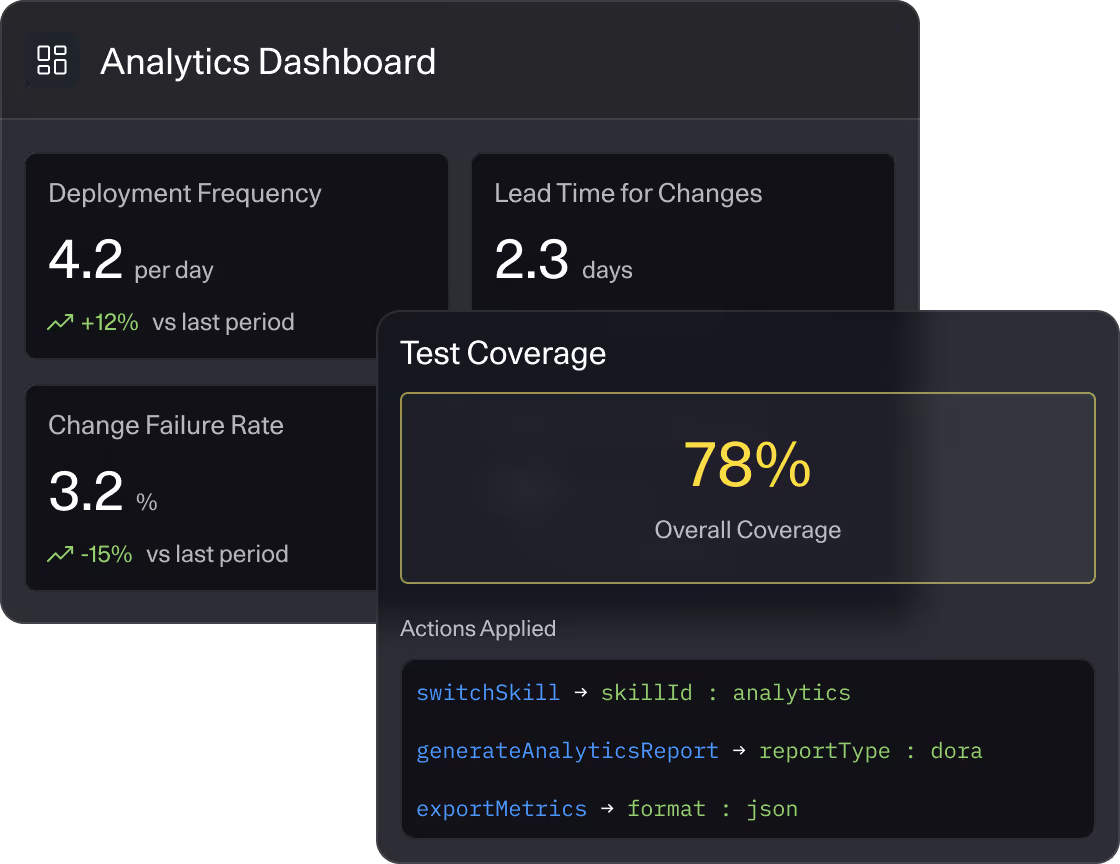
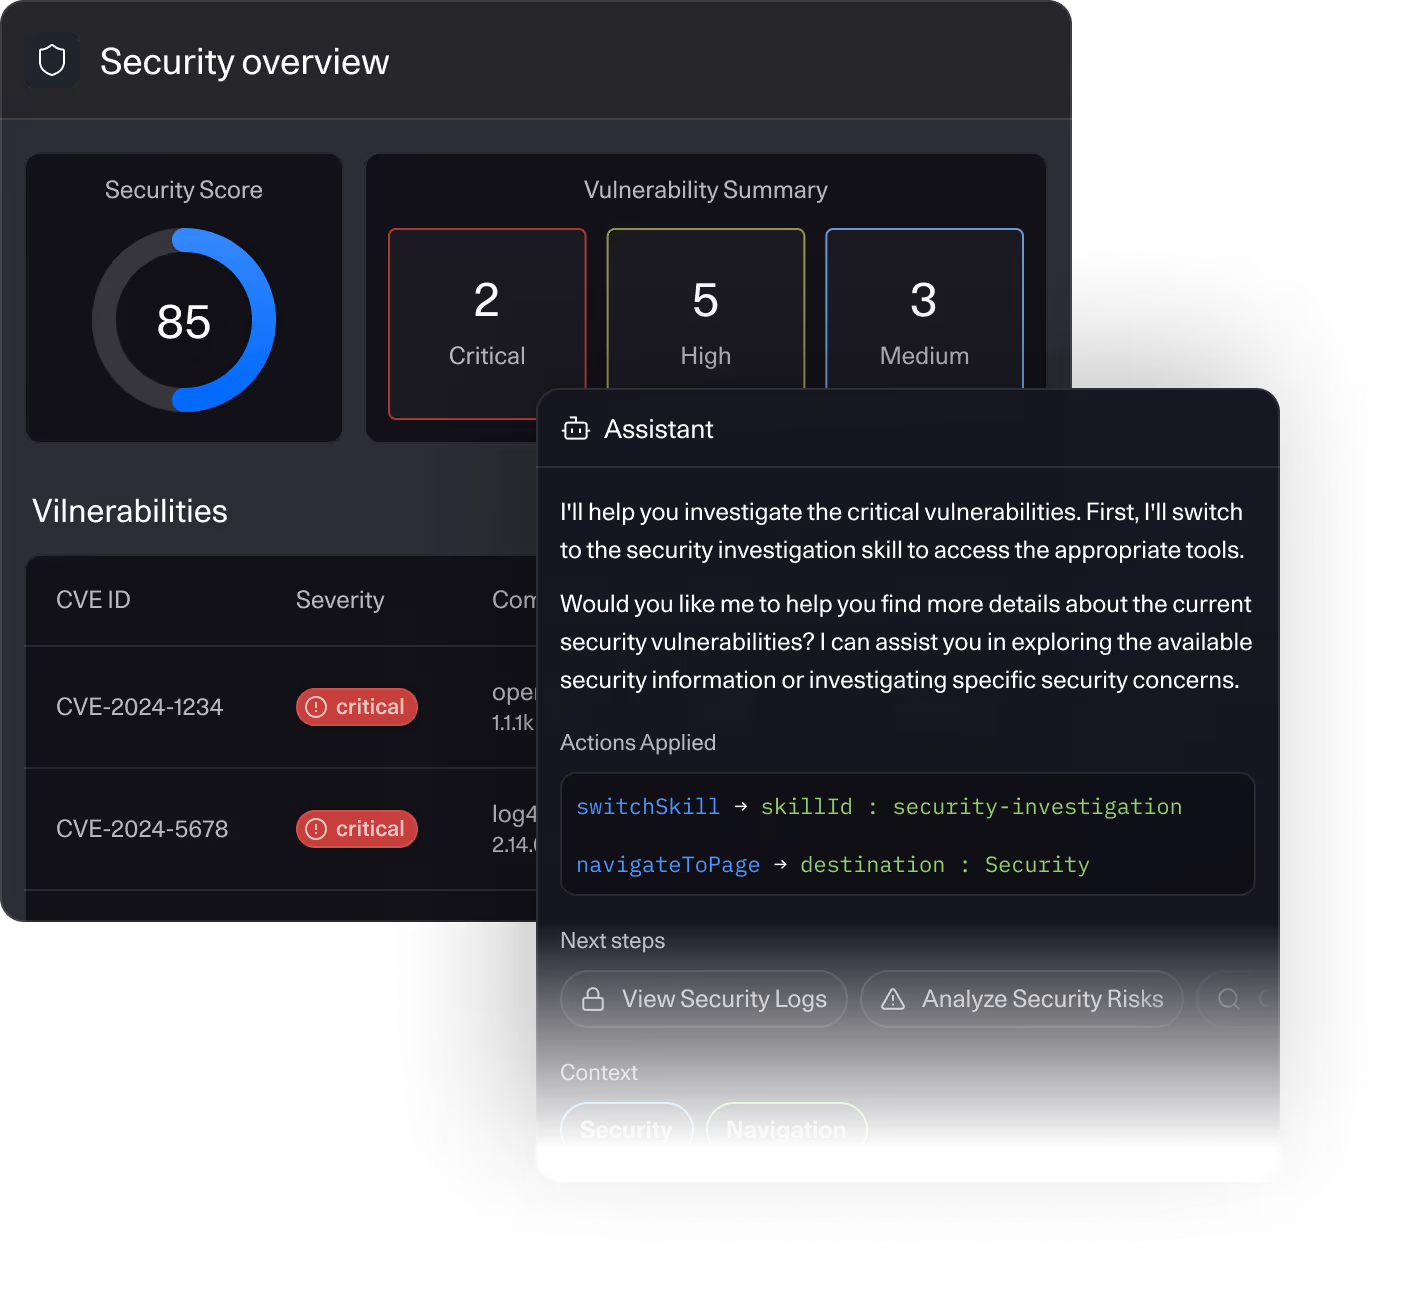
CloudBees Unify is a control plane above Jenkins, GitHub Actions and your supported scanners. Engineers, platform teams and auditors work from one record of each change, from commit to production, whether a person or a coding agent wrote it.
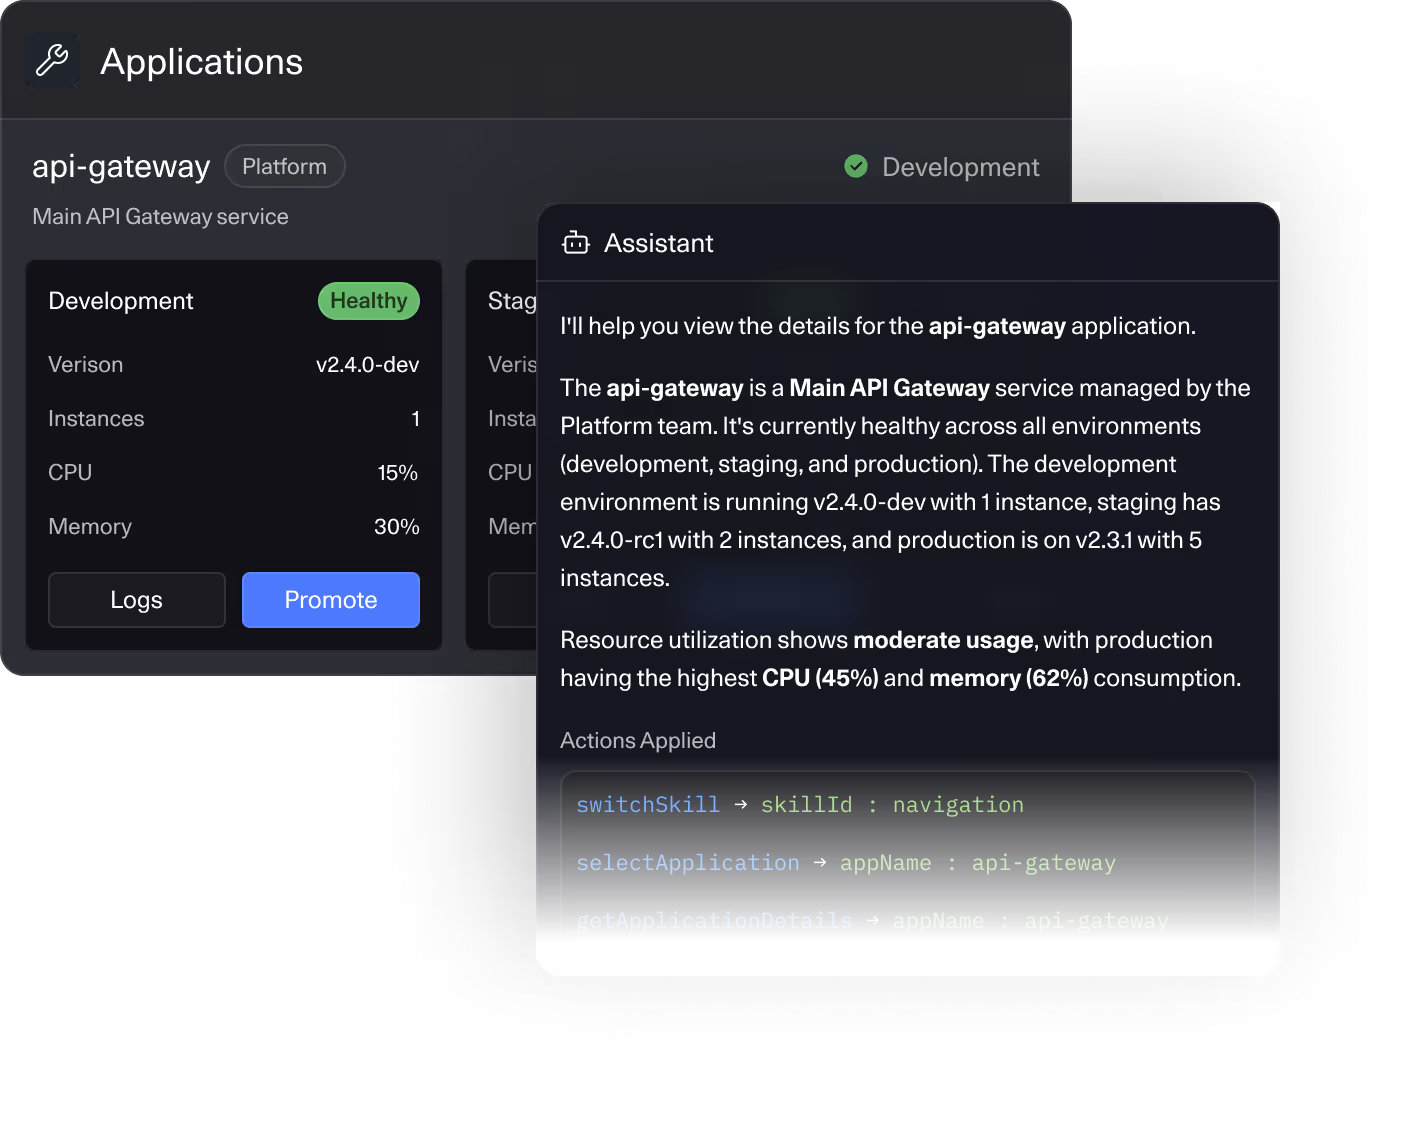
Safe to ship
Releases clear a recorded gate with a named approver, instead of a thumbs-up in Slack. Required checks run inside the workflow, so nobody has to remember them.
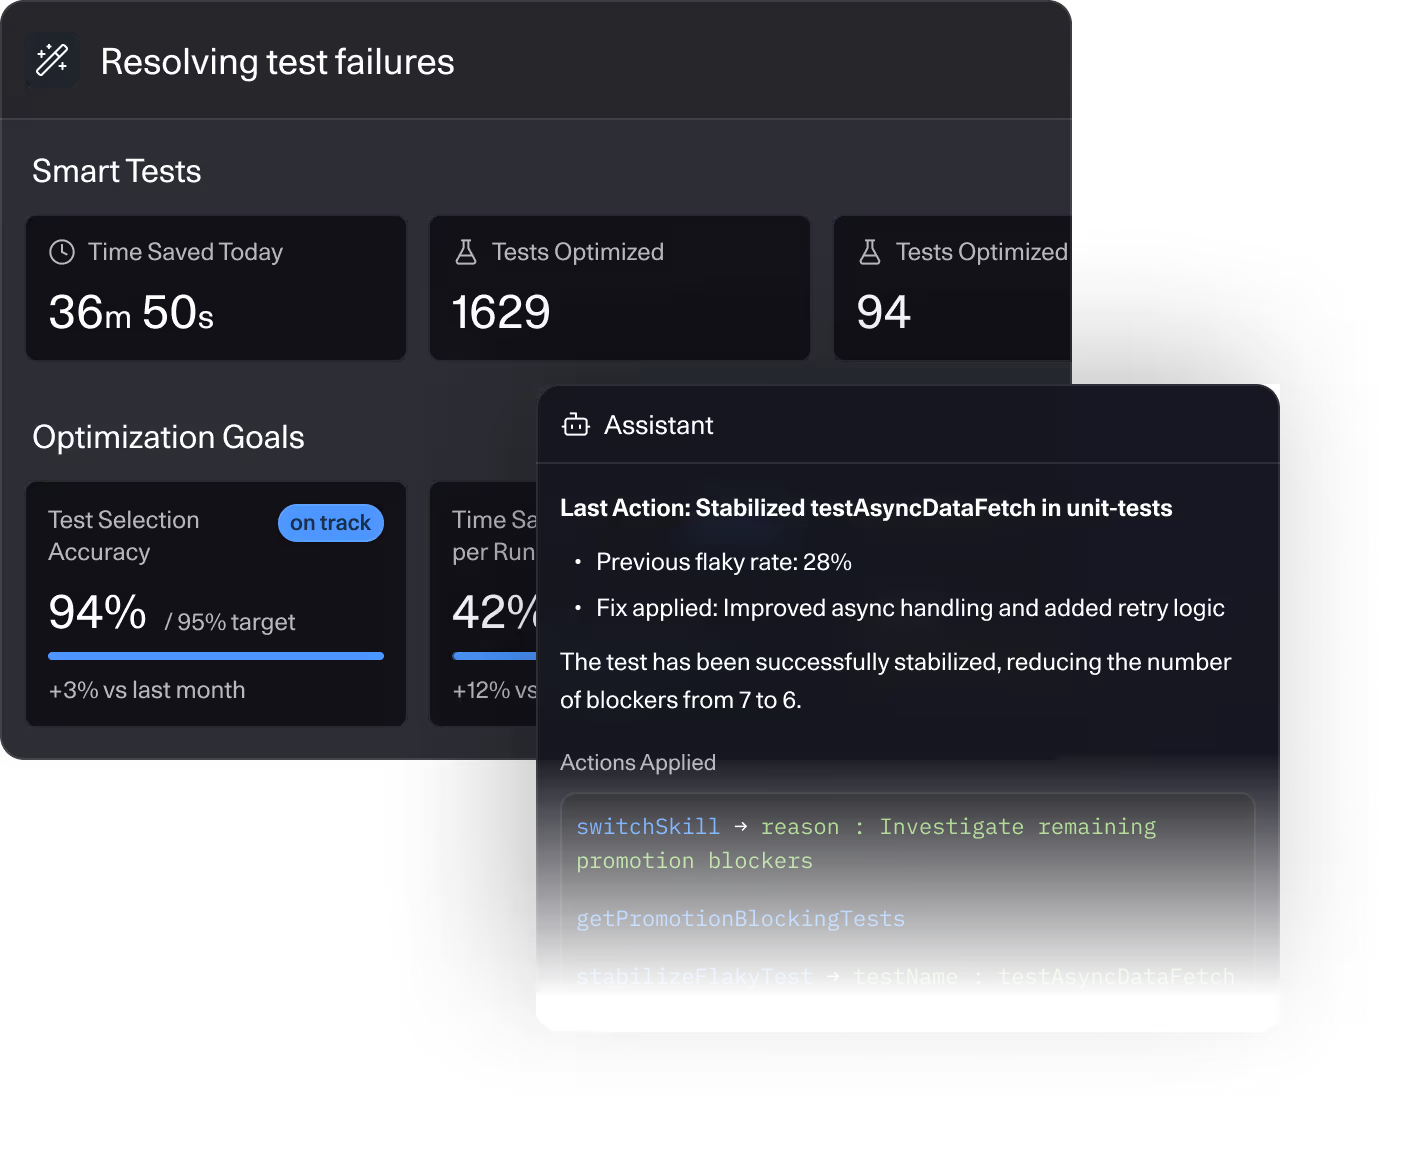
Know your exposure
Findings from your supported scanners land in one deduplicated view, tied to the release and service where each one runs, with a due date by severity.
Audit on demand
Approvals, deployed artifacts and evidence are captured as each release happens. When the auditor asks, you send the report.
What changes for each team

Platform engineering: Keep your pipelines as they are
Connect Jenkins, GitHub Actions and your entire factory without rewriting them.

Platform engineering: Confirm required check ran
Use one place to see whether each required control ran on a release, without opening each tool.

Developers: See what a change touches.
Identify the services and environments behind a change, before you act and after it ships.

AppSec: Work the riskiest findings first
See findings ranked by where they run and when they’re due, so overdue items show up before they miss SLA.

Compliance: Know who approved each release
Tie every production release to the approver’s name, so there’s always an answer to “who decided?”

Download the audit report
Approvals, deployed artifacts and evidence for any release, in one PDF.
What was hard at human speed breaks at agent speed
From CloudBees’ State of Code Abundance 2026 survey of enterprise technology leaders:
93%
have a review process for AI-generated code. Only 56% enforce it consistently.
81%
report more production issues linked to AI-generated code
12%
have anyone who owns AI governance
Trusted by enterprises,
loved by developers

Salesforce migrates DevOps to the cloud with CloudBees CI
Salesforce moved software development to CloudBees CI on Amazon EKS, improving productivity, security, and supporting the continuous delivery of innovative solutions on the Salesforce platform.

Autodesk gets SOC 2 without the burden
With 4,000 engineers and more than 200 applications, Autodesk runs CloudBees CI and meets SOC 2 without the compliance burden.

Acquia brings 16+ Jenkins instances under centralized, compl
Inconsistent security across 16+ Jenkins instances raised FedRAMP concerns. Consolidating on CloudBees CI gave Acquia centralized management and governed CI/CD that meets compliance requirements.
American Express CBT gains competitive advantage with CI/CD
American Express Global Business Travel won the 2019 CloudBees Innovation Award for CI/CD Automation Excellence based on its DevOps transformation.
Find the seams before your agents do
Ninety minutes with your platform, security and compliance leads. We map where your visibility stops, where the critical seams are and what to govern first.
You keep the map either way.


